

TAKE Certified Ethical Hacker 312-49v11 PRACTICE QUESTIONS FOR AMAZING RESULTS
EC-COUNCIL 312-49v11 Exam Dumps Are Essential To Get Good Marks
EC-COUNCIL 312-49v11 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
NEW QUESTION # 62
What happens when a file is deleted by a Microsoft operating system using the FAT file system?
- A. The file is erased but can be recovered partially
- B. A copy of the file is stored and the original file is erased
- C. Only the reference to the file is removed from the FAT and can be recovered
- D. The file is erased and cannot be recovered
Answer: C
NEW QUESTION # 63
BMP (Bitmap) is a standard file format for computers running the Windows operating system.
BMP images can range from black and white (1 bit per pixel) up to 24 bit color (16.7 million colors). Each bitmap file contains a header, the RGBQUAD array, information header, and image data. Which of the following element specifies the dimensions, compression type, and color format for the bitmap?
- A. The RGBQUAD array
- B. Image data
- C. Header
- D. Information header
Answer: D
NEW QUESTION # 64
After a big security incident at a global company, the cybersecurity unit pinpointed the cause as a cleverly designed phishing attempt coupled with an internal attack. The impact of this cybercrime has been detrimental, disrupting normal business operations and theft of sensitive information.
The company needs to assess the most effective measure to minimize the recurrence of such incidents and safeguard its IT infrastructure. What should they prioritize?
- A. Introducing more robust user authentication methods
- B. Strengthening their IT security framework in compliance with relevant policies, standards, and regulations
- C. Enhancing firewall configuration to better filter incoming traffic
- D. Increasing the frequency of their existing routine security audits
Answer: B
NEW QUESTION # 65
A security firm investigating an IoT-based cybercrime involving an Android smartwatch found on the crime scene. The smartwatch is suspected of capturing sensitive information such as PINs and passwords through motion sensors and GPS tracking. The paired smartphone is not available. Which of the following steps should the investigator undertake first to proceed with the forensics process effectively?
- A. Generate forensic images of the evidence found on the crime scene
- B. Identify APIs like Data API, Message API, and Node API on the smartwatch
- C. Look for cloud data and mobile data linked to the smartwatch
- D. Extract data from the smartwatch's memory before it gets volatile
Answer: D
NEW QUESTION # 66
What is a chain of custody?
- A. Chain of custody refers to obtaining preemptive court order to restrict further damage of evidence in electronic seizures
- B. A legal document that demonstrates the progression of evidence as it travels from the original evidence location to the forensic laboratory
- C. It is a search warrant that is required for seizing evidence at a crime scene
- D. It Is a document that lists chain of windows process events
Answer: B
NEW QUESTION # 67
An on-site incident response team is called to investigate an alleged case of computer tampering within their company. Before proceeding with the investigation, the CEO informs them that the incident will be classified as low level. How long will the team have to respond to the incident?
- A. Immediately
- B. Two working days
- C. Four hours
- D. One working day
Answer: D
NEW QUESTION # 68
Computer forensics report provides detailed information on complete computer forensics investigation process. It should explain how the incident occurred, provide technical details of the incident and should be clear to understand. Which of the following attributes of a forensics report can render it inadmissible in a court of law?
- A. It is based on logical assumptions about the incident timeline
- B. It includes metadata about the incident
- C. It maintains a single document style throughout the text
- D. It includes relevant extracts referred to In the report that support analysis or conclusions
Answer: A
NEW QUESTION # 69
When investigating a Windows System, it is important to view the contents of the page or swap file because:
- A. This is the file that windows use to store the history of the last 100 commands that were run from the command line
- B. A Large volume of data can exist within the swap file of which the computer user has no knowledge
- C. Windows stores all of the systems configuration information in this file
- D. This is file that windows use to communicate directly with Registry
Answer: B
NEW QUESTION # 70
Your company's network just finished going through a SAS 70 audit. This audit reported that overall, your network is secure, but there are some areas that needs improvement. The major area was SNMP security. The audit company recommended turning off SNMP, but that is not an option since you have so many remote nodes to keep track of. What step could you take to help secure SNMP on your network?
- A. Block all internal MAC address from using SNMP
- B. Block access to UDP port 171
- C. Block access to TCP port 171
- D. Change the default community string names
Answer: D
NEW QUESTION # 71
During a cybercrime investigation, investigators obtain a warrant to search a suspect's computer system for evidence of hacking activities. As they collect data from the suspect's electronic devices, they inadvertently access information revealing the identities of other users connected to the system.
Which step in the cybercrime investigation process raises concerns related to privacy issues?
- A. Conducting forensic analysis
- B. Implementing network security measures
- C. Obtaining search warrants
- D. Preserving the anonymity of other users
Answer: A
Explanation:
According to theCHFI v11 Regulations, Policies, and Ethicsdomain,privacy issues most commonly arise during the forensic analysis phaseof a cybercrime investigation. While search warrants legally authorize investigators to collect and examine specific digital evidence, they are typicallyscope-limitedto the suspect, systems, data types, and timeframes defined in the warrant.
Duringforensic analysis, investigators may inadvertently encounterpersonal or sensitive information belonging to third parties, such as usernames, email addresses, chat records, credentials, or identifiers of other users connected to the system. CHFI v11 explicitly highlights this phase as legally and ethically sensitive because analysts must ensure thatnon-relevant data and third-party information are handled carefullyto avoid violations of privacy laws and data protection regulations.
Implementing network security measures is a preventive activity, not an investigative one. Obtaining search warrants is a legal safeguard designed to protect privacy, not create privacy concerns. Preserving anonymity is a mitigation action, not the step that introduces the risk.
CHFI v11 stresses the importance ofminimization, access control, proper documentation, and legal oversightduring forensic analysis to prevent misuse or overexposure of unrelated personal data. Failure to manage privacy during this phase can result in legal challenges, evidence exclusion, or regulatory violations.
Therefore, the step that raisesprivacy-related concernsin this scenario isconducting forensic analysis, makingOption Bthe correct and CHFI v11-verified answer.
NEW QUESTION # 72
Subscriber Identity Module (SIM) is a removable component that contains essential information about the subscriber. Its main function entails authenticating the user of the cell phone to the network to gain access to subscribed services. SIM contains a 20-digit long Integrated Circuit Card identification (ICCID) number, identify the issuer identifier Number from the ICCID below.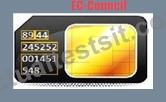
- A. 0
- B. 001451548
- C. 1
- D. 2
Answer: A
NEW QUESTION # 73
Which one of the following is not a first response procedure?
- A. Crack passwords
- B. Take photos
- C. Fill forms
- D. Preserve volatile data
Answer: A
NEW QUESTION # 74
One way to identify the presence of hidden partitions on a suspect's hard drive is to:
- A. It is not possible to have hidden partitions on a hard drive
- B. Examine the LILO and note an H in the partition Type field
- C. Add up the total size of all known partitions and compare it to the total size of the hard drive
- D. Examine the FAT and identify hidden partitions by noting an H in the partition Type field
Answer: C
NEW QUESTION # 75
In a corporate setting, Bob, a software engineer, urgently needs to send an encrypted email containing sensitive project details to Alice, his project manager. Bob carefully composes the email using his corporate email client and clicks send. Little does he know that the corporate email server has been experiencing intermittent connectivity issues.
Amidst sending an urgent email, Bob encounters a delay due to connectivity issues with the corporate email server. At which stage of the email communication process does this delay likely occur?
- A. When decrypting the email message
- B. During the transfer between MTA servers
- C. During the composition of the email
- D. While searching for Alice's email domain
Answer: B
Explanation:
This question aligns with CHFI v11 objectives underNetwork and Web AttacksandEmail Forensics, specifically focusing on understanding how email communication works. According to CHFI v11, the email delivery process involves multiple stages, including message composition by the Mail User Agent (MUA), message submission to the outgoing Mail Transfer Agent (MTA), inter-server transfer between MTAs, and final delivery to the recipient's mailbox via the Mail Delivery Agent (MDA).
Once Bob clicks "send," the email is handed off from his email client (MUA) to the corporate email server's MTA. If the corporate server is experiencing intermittent connectivity issues, delays most commonly occur during thetransfer between MTAs, where the sending MTA attempts to establish an SMTP connection with the recipient's mail server or relay servers. Network instability, DNS delays, or SMTP retry mechanisms can all cause queued messages and delayed delivery at this stage.
Encryption and decryption processes occur locally or at defined endpoints and do not typically introduce network-related delays. Composition is performed entirely on the sender's system, and domain lookups usually happen quickly before transmission. Therefore, in accordance with CHFI v11 email communication fundamentals, the delay is most likely during the transfer between MTA servers.
NEW QUESTION # 76
Detective Harris is leading a digital forensics investigation into a cyberattack on a local bank's database.
During the investigation, Detective Harris emphasizes the importance of maintaining the integrity of the evidence. He instructs his team to follow the established rules of thumb for data acquisition to ensure the admissibility of evidence in court. In Detective Harris's digital forensics investigation of the cyberattack on the bank's database, what step is crucial to preserving the original evidence and ensuring its integrity?
- A. Ignoring the duplication process and proceeding with analysis directly on the original evidence
- B. Performing forensic analysis directly on the original evidence
- C. Creating a duplicate bit-stream image of the suspicious drive or file
- D. Using multiple forensic tools simultaneously for data acquisition
Answer: C
Explanation:
According to the CHFI v11 objectives underData Acquisition Concepts and RulesandDigital Evidence Handling, the most critical step in preserving original evidence integrity is the creation of aduplicate bit- stream imageof the suspect media. A bit-stream image (also known as a forensic image) is an exact sector-by- sector copy of the original storage device, including allocated space, unallocated space, slack space, and hidden data. This ensures that no data is altered, added, or omitted during acquisition.
CHFI v11 clearly states one of the fundamentalrules of thumb for data acquisition:never perform analysis on original evidence. Instead, investigators must work exclusively on verified copies while the original evidence is preserved in a secured state. Hash values are calculated before and after imaging to confirm that the duplicate image is an exact replica, thereby supportingchain of custodyandcourt admissibility.
Options C and D violate forensic best practices by risking accidental modification of the original evidence, which could render it legally inadmissible. Using multiple tools simultaneously (Option B) does not inherently preserve integrity and may introduce inconsistencies if not properly validated.
The CHFI Exam Blueprint v4 emphasizes forensic imaging and validation as mandatory steps in evidence preservation, makingcreating a duplicate bit-stream imagethe correct and exam-aligned answer
NEW QUESTION # 77
Lynne receives the following email:
Dear [email protected]! We are sorry to inform you that your ID has been temporarily frozen due to incorrect or missing information saved at 2016/11/10 20:40:24 You have 24 hours to fix this problem or risk to be closed permanently! To proceed Please Connect >> My Apple ID Thank You The link to My Apple ID shows http://byggarbetsplatsen.se/backup/signon/ What type of attack is this?
- A. Email Spoofing
- B. Phishing
- C. Mail Bombing
- D. Email Spamming
Answer: B
NEW QUESTION # 78
......
Latest EC-COUNCIL 312-49v11 Dumps with Test Engine and PDF (New Questions): https://www.actualtestsit.com/EC-COUNCIL/312-49v11-exam-prep-dumps.html
Pass Your 312-49v11 Exam Easily - Real 312-49v11 Practice Dump Updated: https://drive.google.com/open?id=1Ob3EUv8v4rRYg9iAoraQu22rnUo_eqls