

2022 Realistic 300-730 Dumps Latest Cisco Practice Tests Dumps
300-730 Dumps PDF - 300-730 Real Exam Questions Answers
NEW QUESTION 20
Cisco AnyConnect Secure Mobility Client has been configured to use IKEv2 for one group of users and SSL for another group. When the administrator configures a new AnyConnect release on the Cisco ASA, the IKEv2 users cannot download it automatically when they connect. What might be the problem?
- A. The XML profile is not configured correctly for the affected users.
- B. Client services are not enabled.
- C. Client software updates are not supported with IKEv2.
- D. The new client image does not use the same major release as the current one.
Answer: B
NEW QUESTION 21
Which command automatically initiates a smart tunnel when a user logs in to the WebVPN portal page?
- A. auto-upgrade
- B. auto-start
- C. auto-run
- D. auto-connect
Answer: B
NEW QUESTION 22
Which feature of GETVPN is a limitation of DMVPN and FlexVPN?
- A. design for use over public or private WAN
- B. enabled use of ESP or AH
- C. no requirement for an overlay routing protocol
- D. sequence numbers that enable scalable replay checking
Answer: C
Explanation:
Section: Secure Communications Architectures
NEW QUESTION 23
Which IKE identity does an IOS/IOS-XE headend expect to receive if an IPsec Cisco AnyConnect client uses default settings?
- A. *$DfltlkeldentityS*
- B. *$RemoteAccessVpnClient$*
- C. *$SecureMobilityClient$*
- D. *$AnyConnectClient$*
Answer: D
NEW QUESTION 24
Refer to the exhibit.
Which two tunnel types produce the show crypto ipsec sa output seen in the exhibit? (Choose two.)
- A. FlexVPN
- B. DMVPN
- C. VTI
- D. GRE
- E. crypto map
Answer: B,C
NEW QUESTION 25
Which statement about GETVPN is true?
- A. Group members must acknowledge all KEK and TEK rekeys, regardless of configuration.
- B. The pseudotime that is used for replay checking is synchronized via NTP.
- C. The configuration that defines which traffic to encrypt originates from the key server.
- D. TEK rekeys can be load-balanced between two key servers operating in COOP.
Answer: C
NEW QUESTION 26
Which technology is used to send multicast traffic over a site-to-site VPN?
- A. GRE over IPsec on FTD
- B. GRE tunnel on ASA
- C. IPsec tunnel on FTD
- D. GRE over IPsec on IOS router
Answer: A
Explanation:
Section: Secure Communications Architectures
NEW QUESTION 27
Refer to the exhibit.
All internal clients behind the ASA are port address translated to the public outside interface that has an IP address of 3.3.3.3. Client 1 and client 2 have established successful SSL VPN connections to the ASA.
What must be implemented so that "3.3.3.3" is returned from a browser search on the IP address?
- A. Tunnel Network List Below under Group Policy
- B. Exclude Network List Below under Group Policy
- C. Tunnel All Networks under Group Policy
- D. Same-security-traffic permit inter-interface under Group Policy
Answer: A
NEW QUESTION 28
Refer to the exhibit.
What is configured as a result of this command set?
- A. FlexVPN client profile for IPv6
- B. FlexVPN server to authenticate IPv6 peers by using EAP
- C. FlexVPN server to authorize groups by using an IPv6 external AAA
- D. FlexVPN server for an IPv6 dVTI session
Answer: A
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_ike2vpn/configuration/xe-3s/sec-flex- vpn-xe-3s-book/sec-cfg-flex-clnt.html
NEW QUESTION 29 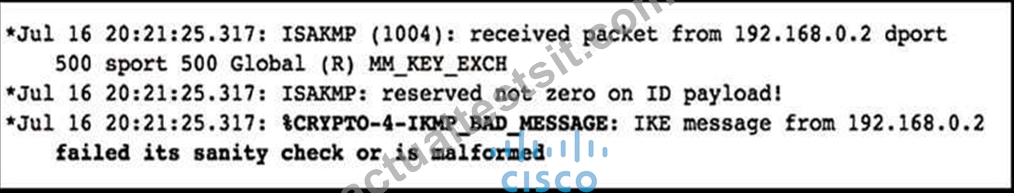
Refer to the exhibit. Which type of mismatch is causing the problem with the IPsec VPN tunnel?
- A. transform set
- B. Phase 1 policy
- C. preshared key
- D. crypto access list
Answer: C
Explanation:
Section: Troubleshooting using ASDM and CLI
Explanation/Reference: https://www.cisco.com/c/en/us/support/docs/security-vpn/ipsec-negotiation-ike-protocols/5409- ipsec-debug-00.html#ike
NEW QUESTION 30 
Refer to the exhibit. Based on the exhibit, why are users unable to access CCNP Webserver bookmark?
- A. The ASA cannot resolve the URL.
- B. The bookmark has been disabled.
- C. The user cannot access the URL.
- D. The URL is being blocked by a WebACL.
Answer: B
Explanation:
Section: Remote access VPNs
NEW QUESTION 31
An engineer is troubleshooting a new DMVPN setup on a Cisco IOS router. After the show crypto isakmp sa command is issued, a response is returned of "MM_NO_STATE." Why does this failure occur?
- A. Tunnel protection is not applied to the DMVPN tunnel.
- B. The ISAKMP policy priority values are invalid.
- C. The Phase 1 policy does not match on both devices.
- D. ESP traffic is being dropped.
Answer: D
Explanation:
Section: Troubleshooting using ASDM and CLI
NEW QUESTION 32
A Cisco ASA is configured in active/standby mode. What is needed to ensure that Cisco AnyConnect users can connect after a failover event?
- A. Configure a backup server in the XML profile.
- B. The vpnsession-db must be cleared manually.
- C. AnyConnect client must point to the standby IP address.
- D. AnyConnect images must be uploaded to both failover ASA devices.
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa90/configuration/guide/asa_90_cli_config/ ha_active_standby.html
NEW QUESTION 33
Refer to the exhibit.
A user is connecting from behind a PC with a private IP Address. Their ISP provider is blocking TCP port 443. Which AnyConnect XML configuration will allow the user to establish a connection with the ASA?

- A. Option C
- B. Option B
- C. Option A
- D. Option D
Answer: D
NEW QUESTION 34
Refer to the exhibit.
An SSL client is connecting to an ASA headend. The session fails with the message "Connection attempt has timed out. Please verify Internet connectivity." Based on how the packet is processed, which phase is causing the failure?
- A. phase 4: ACCESS-LIST
- B. phase 3: UN-NAT
- C. phase 5: NAT
- D. phase 9: rpf-check
Answer: B
NEW QUESTION 35 
Refer to the exhibit. Cisco AnyConnect must be set up on a router to allow users to access internal servers
192.168.0.10 and 192.168.0.11. All other traffic should go out of the client's local NIC. Which command accomplishes this configuration?
- A. svc split include 192.168.0.0 255.255.255.0
- B. svc split include acl CCNP
- C. svc split exclude acl CCNP
- D. svc split exclude 192.168.0.0 255.255.255.0
Answer: B
Explanation:
Section: Secure Communications Architectures
Explanation/Reference:
NEW QUESTION 36
In order to enable FlexVPN to use a AAA attribute list, which two tasks must be performed? (Choose two.)
- A. Set the maximum segment size.
- B. Verify that clients are using the correct authorization policy.
- C. Define the RADIUS server.
- D. Define the AAA server.
- E. Assign the list to an authorization policy.
Answer: B,E
NEW QUESTION 37
A company's remote locations connect to the data centers via MPLS. A new request requires that unicast and multicast traffic that exits in the remote locations be encrypted. Which non-tunneled technology should be used to satisfy this requirement?
- A. FlexVPN
- B. SSL
- C. DMVPN
- D. GETVPN
Answer: D
NEW QUESTION 38
An engineer is troubleshooting a new DMVPN setup on a Cisco IOS router. After the show crypto isakmp sa command is issued, a response is returned of "MM_NO_STATE." Why does this failure occur?
- A. Tunnel protection is not applied to the DMVPN tunnel.
- B. The ISAKMP policy priority values are invalid.
- C. The Phase 1 policy does not match on both devices.
- D. ESP traffic is being dropped.
Answer: D
NEW QUESTION 39
Refer to the exhibit.
The customer must launch Cisco AnyConnect in the RDP machine. Which IOS configuration accomplishes this task?
- A. Option C
- B. Option D
- C. Option B
- D. Option A
Answer: A
NEW QUESTION 40
A Cisco ASA is configured in active/standby mode. What is needed to ensure that Cisco AnyConnect users can connect after a failover event?
- A. Configure a backup server in the XML profile.
- B. The vpnsession-db must be cleared manually.
- C. AnyConnect client must point to the standby IP address.
- D. AnyConnect images must be uploaded to both failover ASA devices.
Answer: D
Explanation:
Section: Secure Communications Architectures
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/asa/asa90/configuration/guide/asa_90_cli_config/ ha_active_standby.html
NEW QUESTION 41
Refer to the exhibit.
Which type of VPN is being configured, based on the partial configuration snippet?
- A. GET VPN with dual group member
- B. FlexVPN load balancer
- C. GET VPN with COOP key server
- D. FlexVPN backup gateway
Answer: C
NEW QUESTION 42
Where must an engineer configure a preshared key for a site-to-site VPN tunnel configured on a Cisco ASA?
- A. tunnel group
- B. crypto map
- C. group policy
- D. isakmp policy
Answer: A
NEW QUESTION 43
Which technology is used to send multicast traffic over a site-to-site VPN?
- A. GRE over IPsec on FTD
- B. GRE tunnel on ASA
- C. IPsec tunnel on FTD
- D. GRE over IPsec on IOS router
Answer: A
NEW QUESTION 44 
Refer to the exhibit. Which two commands under the tunnel-group webvpn-attributes result in a Cisco AnyConnect user receiving the AnyConnect prompt in the exhibit? (Choose two.)
- A. authentication aaa
- B. group-policy General internal
- C. authentication certificate
- D. group-alias General enable
- E. group-url https://172.16.31.10/General enable
Answer: B,D
Explanation:
Section: Remote access VPNs
NEW QUESTION 45
......
300-730 Premium Exam Engine pdf Download: https://www.actualtestsit.com/Cisco/300-730-exam-prep-dumps.html
300-730 Exam [2022] Dumps Cisco PDF Questions: https://drive.google.com/open?id=1CITjsZXHonPCqGpJoB1ORNw23XxCFODt