

Essentials Dumps Updated Apr 12, 2023 Practice Test and 75 unique questions
2023 Latest 100% Exam Passing Ratio - Essentials Dumps PDF
The WatchGuard Essentials Exam is a vendor-specific certification that is recognized globally. It is offered by WatchGuard Technologies, a leading provider of network security solutions. The exam is designed to validate the skills and knowledge required to install, configure, and manage WatchGuard Firebox appliances. It ensures that candidates have a thorough understanding of the product features and capabilities and can effectively troubleshoot common issues.
To take the WatchGuard Essentials Exam, candidates must have a good understanding of TCP/IP networking and basic network security concepts. They should also have some experience with WatchGuard firewalls and the Fireware operating system. The exam is computer-based and consists of multiple-choice questions. Candidates have 90 minutes to complete the exam and must score at least 70% to pass. Successful candidates will receive a WatchGuard Certified System Professional (WCSP) certification, which demonstrates their expertise in WatchGuard firewall technology.
To prepare for the WatchGuard Essentials (Fireware Essentials) Certification Exam, candidates can take advantage of a range of study materials, including online courses, practice exams, and study guides. These resources cover all the topics that are included in the exam and provide candidates with a solid foundation in WatchGuard firewall administration. With the right preparation, candidates can pass the exam and earn their certification, demonstrating their expertise in WatchGuard firewall management and administration.
NEW QUESTION # 20
Which diagnostic tasks can you run from the Traffic Monitor tab of Firebox System Manager? (Select four.)
- A. Traceroute
- B. DNS lookup
- C. TCP dump
- D. Ping
- E. Reputation lookup
- F. MAC address lookup
Answer: A,B,C,D
Explanation:
Explanation/Reference:
From Firebox System Manager, you can run diagnostic tasks to review information in all the log messages from your Firebox or XTM device. This can help you debug problems on your network.
1. On the Traffic Monitor tab, right-click a message and select Diagnostic Tasks.
Or, select Tools > Diagnostic Tasks.
2. From the Task drop-down list, select the task to run.
Ping IPv4
Ping IPv6
traceroute
DNS Lookup
TCP Dump
Reference: http://watchguard.com/help/docs/wsm/xtm_11/en-us/content/en-us/fsm/ log_message_learn_more_wsm.html
NEW QUESTION # 21
Match each type of NAT with the correct description:
Changes and routes all incoming and outgoing packets sent from one range of addresses to a different range of addresses. (Choose one)
- A. NAT Loopback
- B. Dynamic NAT
- C. 1-to1 NAT
Answer: C
Explanation:
When you enable 1-to-1 NAT, the Firebox changes and routes all incoming and outgoing packets sent from one range of addresses to a different range of addresses.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 74
NEW QUESTION # 22
Only 50 clients on the trusted network of your Firebox can connect to the Internet at the same time. What could cause this? (Select one.)
- A. The Outgoing policy allows a maximum of 50 client connections.
- B. The device feature key allows a maximum of 50 client connections.
- C. TheLiveSecurity feature key is expired.
- D. The DHCP address pool on the trusted interface has only 50 IP addresses.
Answer: D
NEW QUESTION # 23
HOTSPOT
Match the monitoring tool to the correct task: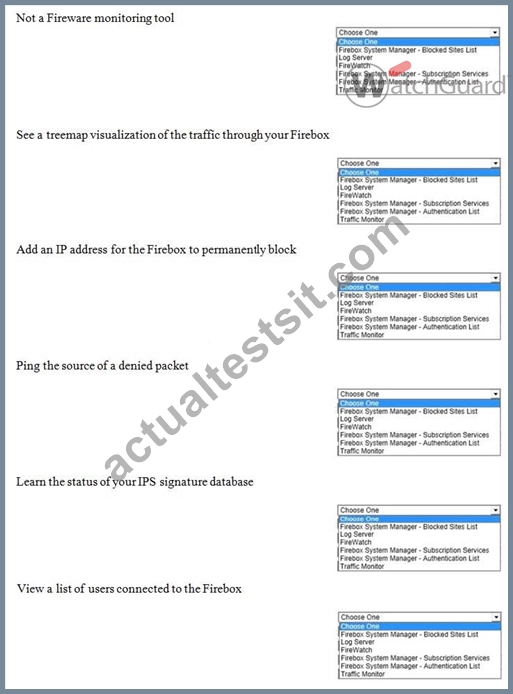
Answer:
Explanation: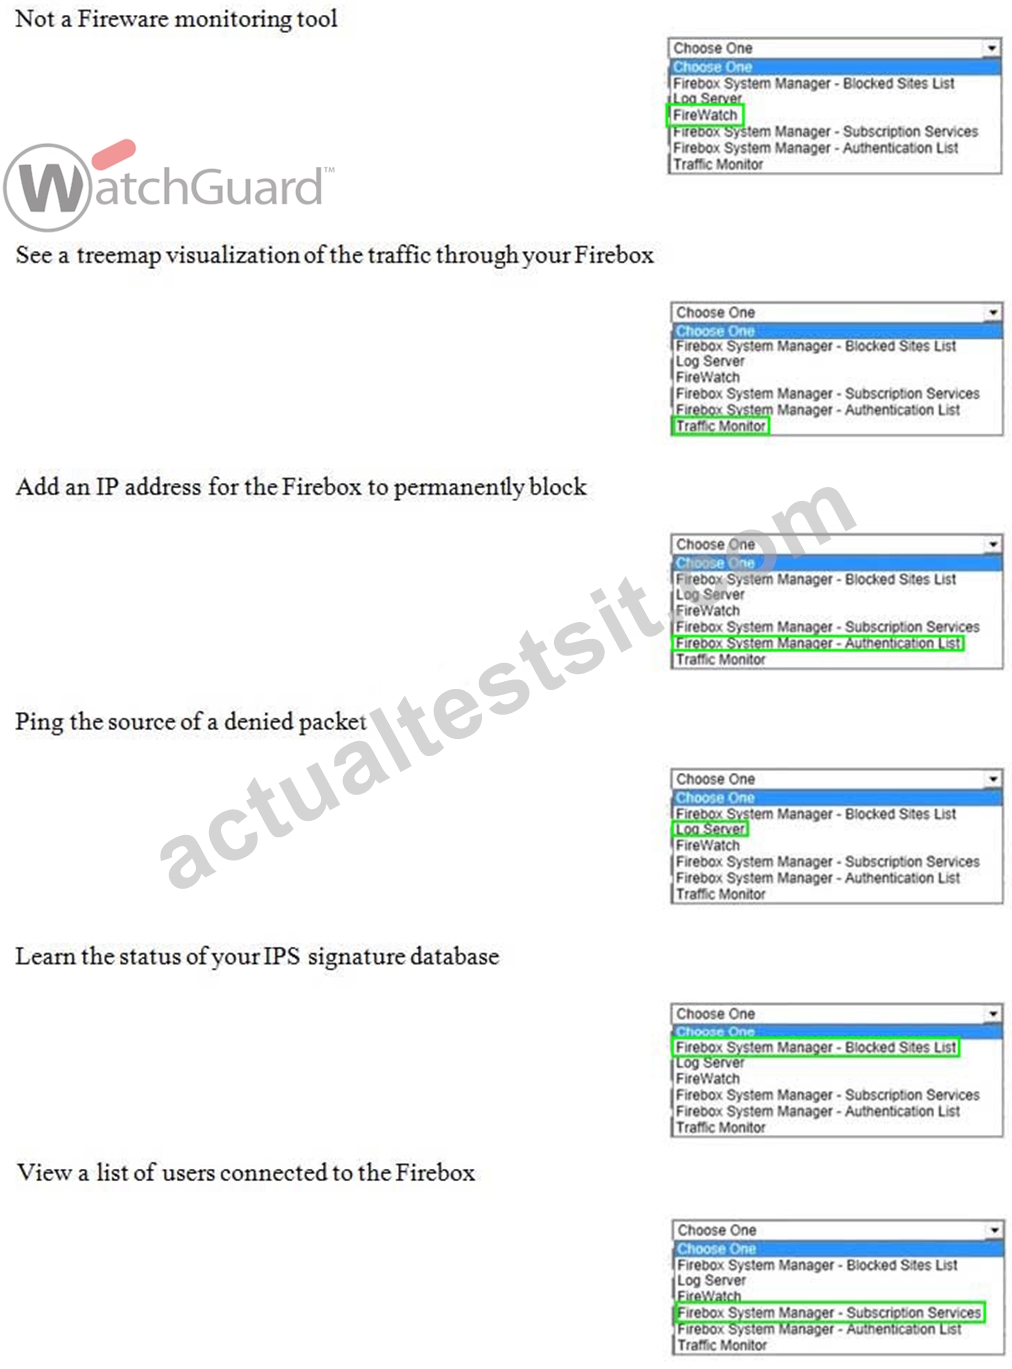
Explanation:
Firewatch Traffic Monitor Firebox system Manager - Authentication List Log Server Firbox System Manager - Blocked State List Firebox System Manager - Subscription Services
NEW QUESTION # 24
Match each type of NAT with the correct description:
Changes and routes all incoming and outgoing packets sent from one range of addresses to a different range of addresses. (Choose one)
- A. NAT Loopback
- B. Dynamic NAT
- C. 1-to1 NAT
Answer: C
Explanation:
Explanation/Reference:
When you enable 1-to-1 NAT, the Firebox changes and routes all incoming and outgoing packets sent from one range of addresses to a different range of addresses.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 74
NEW QUESTION # 25
You need to create an HTTP-proxy policy to a specific domain for software updates (example.com). The update site has multiple subdomains and dynamic IP addresses on a content delivery network. Which of these options is the best way to define the destination in your HTTP-proxy policy? (Select one.)
- A. Add IP addresses that correspond to each software update server in the domain.
- B. Configure a host name forupdate.example.com.
- C. Configure an FQDN for*.example.com.
- D. Create an alias for all subdomains and known IP addresses forexample.com.
Answer: C
Explanation:
http://www.watchguard.com/help/docs/fireware/11/en-US/Content/en-US/policies/fqdn_about_c.html
NEW QUESTION # 26
Your company denies downloads of executable files from all websites. What can you do to allow users on the network to download executable files from the company's remote website? (Select one.)
- A. Add an HTTP proxy exception for the company's remote website.
- B. Create a WebBlocker exception to allow access to the company's remote website.
- C. Configure HTTP Request > URL Paths to allow the company's remote website.
- D. Create a Blocked Sites exception.
- E. Create an IPS exception.
Answer: A
NEW QUESTION # 27
You can configure your Firebox to automatically redirect users to the Authentication Portal page.
- A. True
- B. False
Answer: A
NEW QUESTION # 28
Match each WatchGuard Subscription Service with its function.
Uses full-system emulation analysis to identify characteristics and behavior of zero-day malware. (Choose one).
- A. Gateway / Antivirus
- B. Data Loss Prevention DLP
- C. Quarantine Server
- D. Spam Blocker
- E. Reputation Enable Defense RED
- F. APT Blocker
- G. Intrusion Prevention Server IPS
- H. Application Control
- I. WebBlocker
Answer: F
Explanation:
Explanation/Reference:
APT Blocker is intended to stop malware and zero-day threats that are trying to invade an organization's network.
APT Blocker uses a next-gen sandbox to get detailed views into the execution of a malware program. After first running through other security services, files are fingerprinted and checked against an existing database - first on the appliance and then in the cloud. If the file has never been seen before, it is analyzed using the system emulator, which monitors the execution of all instructions. It can spot the evasion techniques that other sandboxes miss.
Reference: http://www.watchguard.com/wgrd-products/security-modules/apt-blocker
NEW QUESTION # 29
Match each WatchGuard Subscription Service with its function.
Uses full-system emulation analysis to identify characteristics and behavior of zero-day malware. (Choose one).
- A. Gateway / Antivirus
- B. Quarantine Server
- C. Spam Blocker
- D. Reputation Enable Defense RED
- E. APT Blocker
- F. Intrusion Prevention Server IPS
- G. Application Control
- H. WebBlocker
- I. DataLoss Prevention DLP
Answer: E
Explanation:
APT Blocker is intended to stop malware and zero-day threats that are trying to invade anorganization's network.
APT Blocker uses a next-gen sandbox to get detailed views into the execution of a malware program. After first running through other security services, files are fingerprinted and checked against an existing database - first on theappliance and then in the cloud. If the file has never been seen before, it is analyzed using the system emulator, which monitors the execution of all instructions. It can spot the evasion techniques that other sandboxes miss.
Reference:http://www.watchguard.com/wgrd-products/security-modules/apt-blocker
NEW QUESTION # 30
In the default Firebox configuration file, which policies control management access to the device? (Select two.)
- A. WatchGuard
- B. FTP
- C. WatchGuard Web UI
- D. Ping
- E. Outgoing
Answer: A,C
Explanation:
Ping is generated by default as the explanation states but Ping does not manage the device. The policies that manage the device are WatchGuard & WatchGuard Web UI
NEW QUESTION # 31
After you enable Gateway AntiVirus, IPS, or Application control, how can you make sure the services protect your network from the latest known threats? (Select one.)
- A. Enable default packet handling.
- B. Enable automatic signature updates.
- C. Configure reputation Enabled Defense.
- D. Enable HTTPS deep inspection.
Answer: B
NEW QUESTION # 32
You need to create an HTTP-proxy policy to a specific domain for software updates (example.com). The update site has multiple subdomains and dynamic IP addresses on a content delivery network. Which of these options is the best way to define the destination in your HTTP-proxy policy? (Select one.)
- A. Configure a host name for update.example.com.
- B. Add IP addresses that correspond to each software update server in the domain.
- C. Create an alias for all subdomains and known IP addresses for example.com.
- D. Configure an FQDN for *.example.com.
Answer: B
NEW QUESTION # 33
Which diagnostic tasks can you run from the Traffic Monitor tab of Firebox System Manager? (Select four.)
- A. Traceroute
- B. DNSlookup
- C. TCP dump
- D. Ping
- E. Reputation lookup
- F. MAC address lookup
Answer: A,B,C,D
Explanation:
From Firebox System Manager, you can run diagnostic tasks to review information in all the log messages from your Firebox or XTM device. This can help you debug problems on your network.
1.On the Traffic Monitor tab, right-click a message and select Diagnostic Tasks. Or, select Tools > Diagnostic Tasks.
2.From the Task drop-down list, select the task to run. Ping IPv4 Ping IPv6 traceroute DNS Lookup TCP Dump
Reference:http://watchguard.com/help/docs/wsm/xtm_11/en-us/content/enus/fsm/log_message_learn_more_wsm.html
NEW QUESTION # 34
Match each WatchGuard Subscription Service with its function.
Controls access to website based on content categories. . (Choose one).
- A. Explanation:
WebBlocker controls access to the good and bad places that are reachable on the web,preventing users from gaining access to sites that have evil intentions.
If you configure WebBlocker to use the Websense cloud for WebBlocker lookups, WebBlocker uses the Websense content categories. A web site is added to a category when the content of the web site meets the criteria for the content category.
Reference:http://www.tomsitpro.com/articles/network-security-solutions-guide, 2-866-6.html
QUESTIONNO: 74
Match each type of NAT with the correct description:
Allows a user on the trusted or optional network to connect to a public server that is on the same physical Firebox interface by its public IP address or domain name. (Choose one)
A. 1-to1 NAT
B. Dynamic NAT
C. NAT Loopback - B. Gateway / Antivirus
- C. Reputation Enable Defense RED
- D. Intrusion Prevention Server IPS
- E. Application Control
- F. WebBlocker
Answer: F
Explanation:
NAT loopback allows a user on the trusted or optional networks to get access to a public server that is on the same physical Firebox or XTM device interface by its public IP address or domain name.
Reference:http://www.watchguard.com/help/docs/wsm/11/en-US/index_Left.html#CSHID=en-US%2Fnat%2Fnat_loopback_c.html|StartTopic=Content%2FenUS%2Fnat%2Fnat_loopback_c.html
NEW QUESTION # 35
While troubleshooting a branch office VPN tunnel, you see this log message:
2014-07-23 12:29:15 iked (203.0.113.10<->203.0.113.20) Peer proposes phase one encryption 3DES, expecting AES What settings could you modify in the local device configuration to resolve this issue? (Select one.)
- A. BOVPN-Allow policies
- B. BOVPN Tunnel Route settings
- C. BOVPN Tunnel settings
- D. BOVPN Gateway settings
Answer: D
Explanation:
The WatchGuard BOVPN settings error in this example states phase one encryption. Only the BOVPN Gateway settings can specify phase one settings. BOVPN Tunnel settings specify phase 2 settings.
NEW QUESTION # 36
......
Verified Essentials dumps Q&As - 100% Pass from ActualTestsIT: https://www.actualtestsit.com/WatchGuard/Essentials-exam-prep-dumps.html
Pass Exam With Full Sureness - Essentials Dumps with 75 Questions: https://drive.google.com/open?id=1TEf3mfDngIrWMCd7NL-bcMGLD81nhlzt